The world of IT security has changed dramatically in the past year, but which changes really matter, and how should companies respond in order to keep their employees and data safe?
A recent Tanium webinar (opens in a new tab), "The Secrets of High-Speed Threat Detection Using Petabytes of Data," featured experts from Accenture, Google and Tanium. They offered a bracing look at the shifting landscape for IT security, identifying new threats and offering guidance for protecting enterprise assets, even when most employees are working from home.
The webinar also included a demonstration of the joint solution of the Tanium Platform with Google Chronicle, Google’s cloud-based platform for collecting and analyzing petabytes of telemetry (opens in a new tab) data in real time to detect and remediate security threats on corporate networks.
Attacks are up and attack surfaces are larger
IT security has probably changed forever as a result of so many people working from home during the pandemic, says Nick Taylor, managing director and UKI security lead for Accenture (opens in a new tab). The shift to remote work and the accompanying increased reliance on cloud services have accelerated an IT transformation that was already underway.
Now that transformation is maturing into a new paradigm of highly distributed workforces and increased reliance on partner networks. Security teams need to adjust their investments and processes accordingly, or they’ll fall victim to new forms of attack and new types of vulnerabilities.
In a world when everyone’s working from home, corporate data and devices are exposed in ways they never have been before. According to Taylor, home networks are about 3.5 times as porous as corporate networks, which means that any endpoint in a home office is at much greater risk than the same endpoint when it was in a corporate office.
Attackers are taking advantage of the chaos created by the pandemic. Taylor noted that:
From industry surveys and insights from Accenture’s network of about 90 CISOs, Taylor shared these troubling numbers:
Accenture’s advice? First, focus on people being the first line of defense. Give employees the training they need to reduce the chance of them making dangerous mistakes, and help them feel part of the company overall even while they’re working from home.
Also, take advantage of solutions like that offered by Tanium and Google for gaining visibility into endpoint threats, so your IT organization can respond quickly when threats arrive.
Detecting and remediating endpoint threats with Tanium and Google Chronicle
Organizations interested in following Accenture’s advice can take advantage of a new Tanium and Google solution for unified endpoint management and Zero Trust initiatives (opens in a new tab).
This new offering (opens in a new tab), sold by Tanium, integrates Tanium’s Threat Response (opens in a new tab) with Chronicle (opens in a new tab), Google Cloud’s security analytics platform, and helps enterprises detect, investigate and scope advanced, long-lived attacks (advanced persistent threats or APTs).
The integrated offering is especially useful for helping security analysts hunt for advanced persistent threats (opens in a new tab) — threats that might be lingering undetected on a network for hundreds of days.
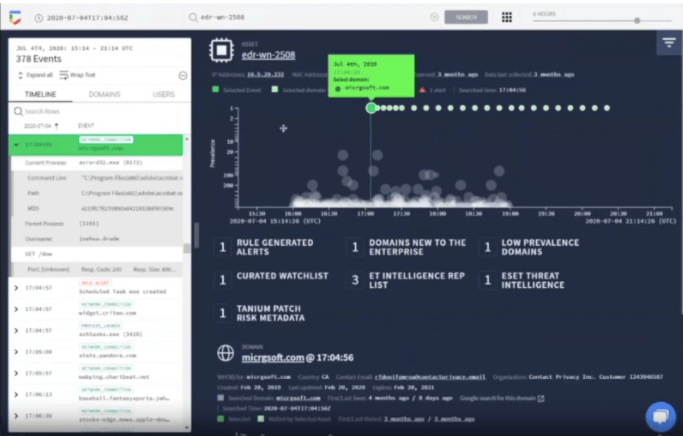
Figure 1. Through its integration with the Tanium Platform, Google Chronicle helps security analysts explore endpoint telemetry data along with updated threat intelligence feeds. Analysts can quickly mitigate threats involving remote endpoints, even in a WFH environment.
Google Chronicle stores a petabyte of endpoint telemetry data streamed from Tanium agents, providing an entire year’s worth of data. Using this massive store of data, analysts can quickly correlate events to identify attacks that would otherwise evade detection. Chronicle’s search technology returns query results instantly, so analysts can investigate and characterize threats as quickly and possible.
For example, a security analyst can use Tanium and Chronicle to investigate activities such as a DNS request for a suspicious domain and to discover any related activity going back one year.
Once the request for the suspicious domain is identified, the analyst can use the Tanium platform to immediately quarantine the affected endpoint, containing the threat.
Watch the webinar (opens in a new tab) with Accenture, Google, and Tanium to learn more about how you can protect your remote workforce from cybercrime.
To learn more about Tanium’s partnership with Google, read our recent press release (opens in a new tab).