Topic
Tech News
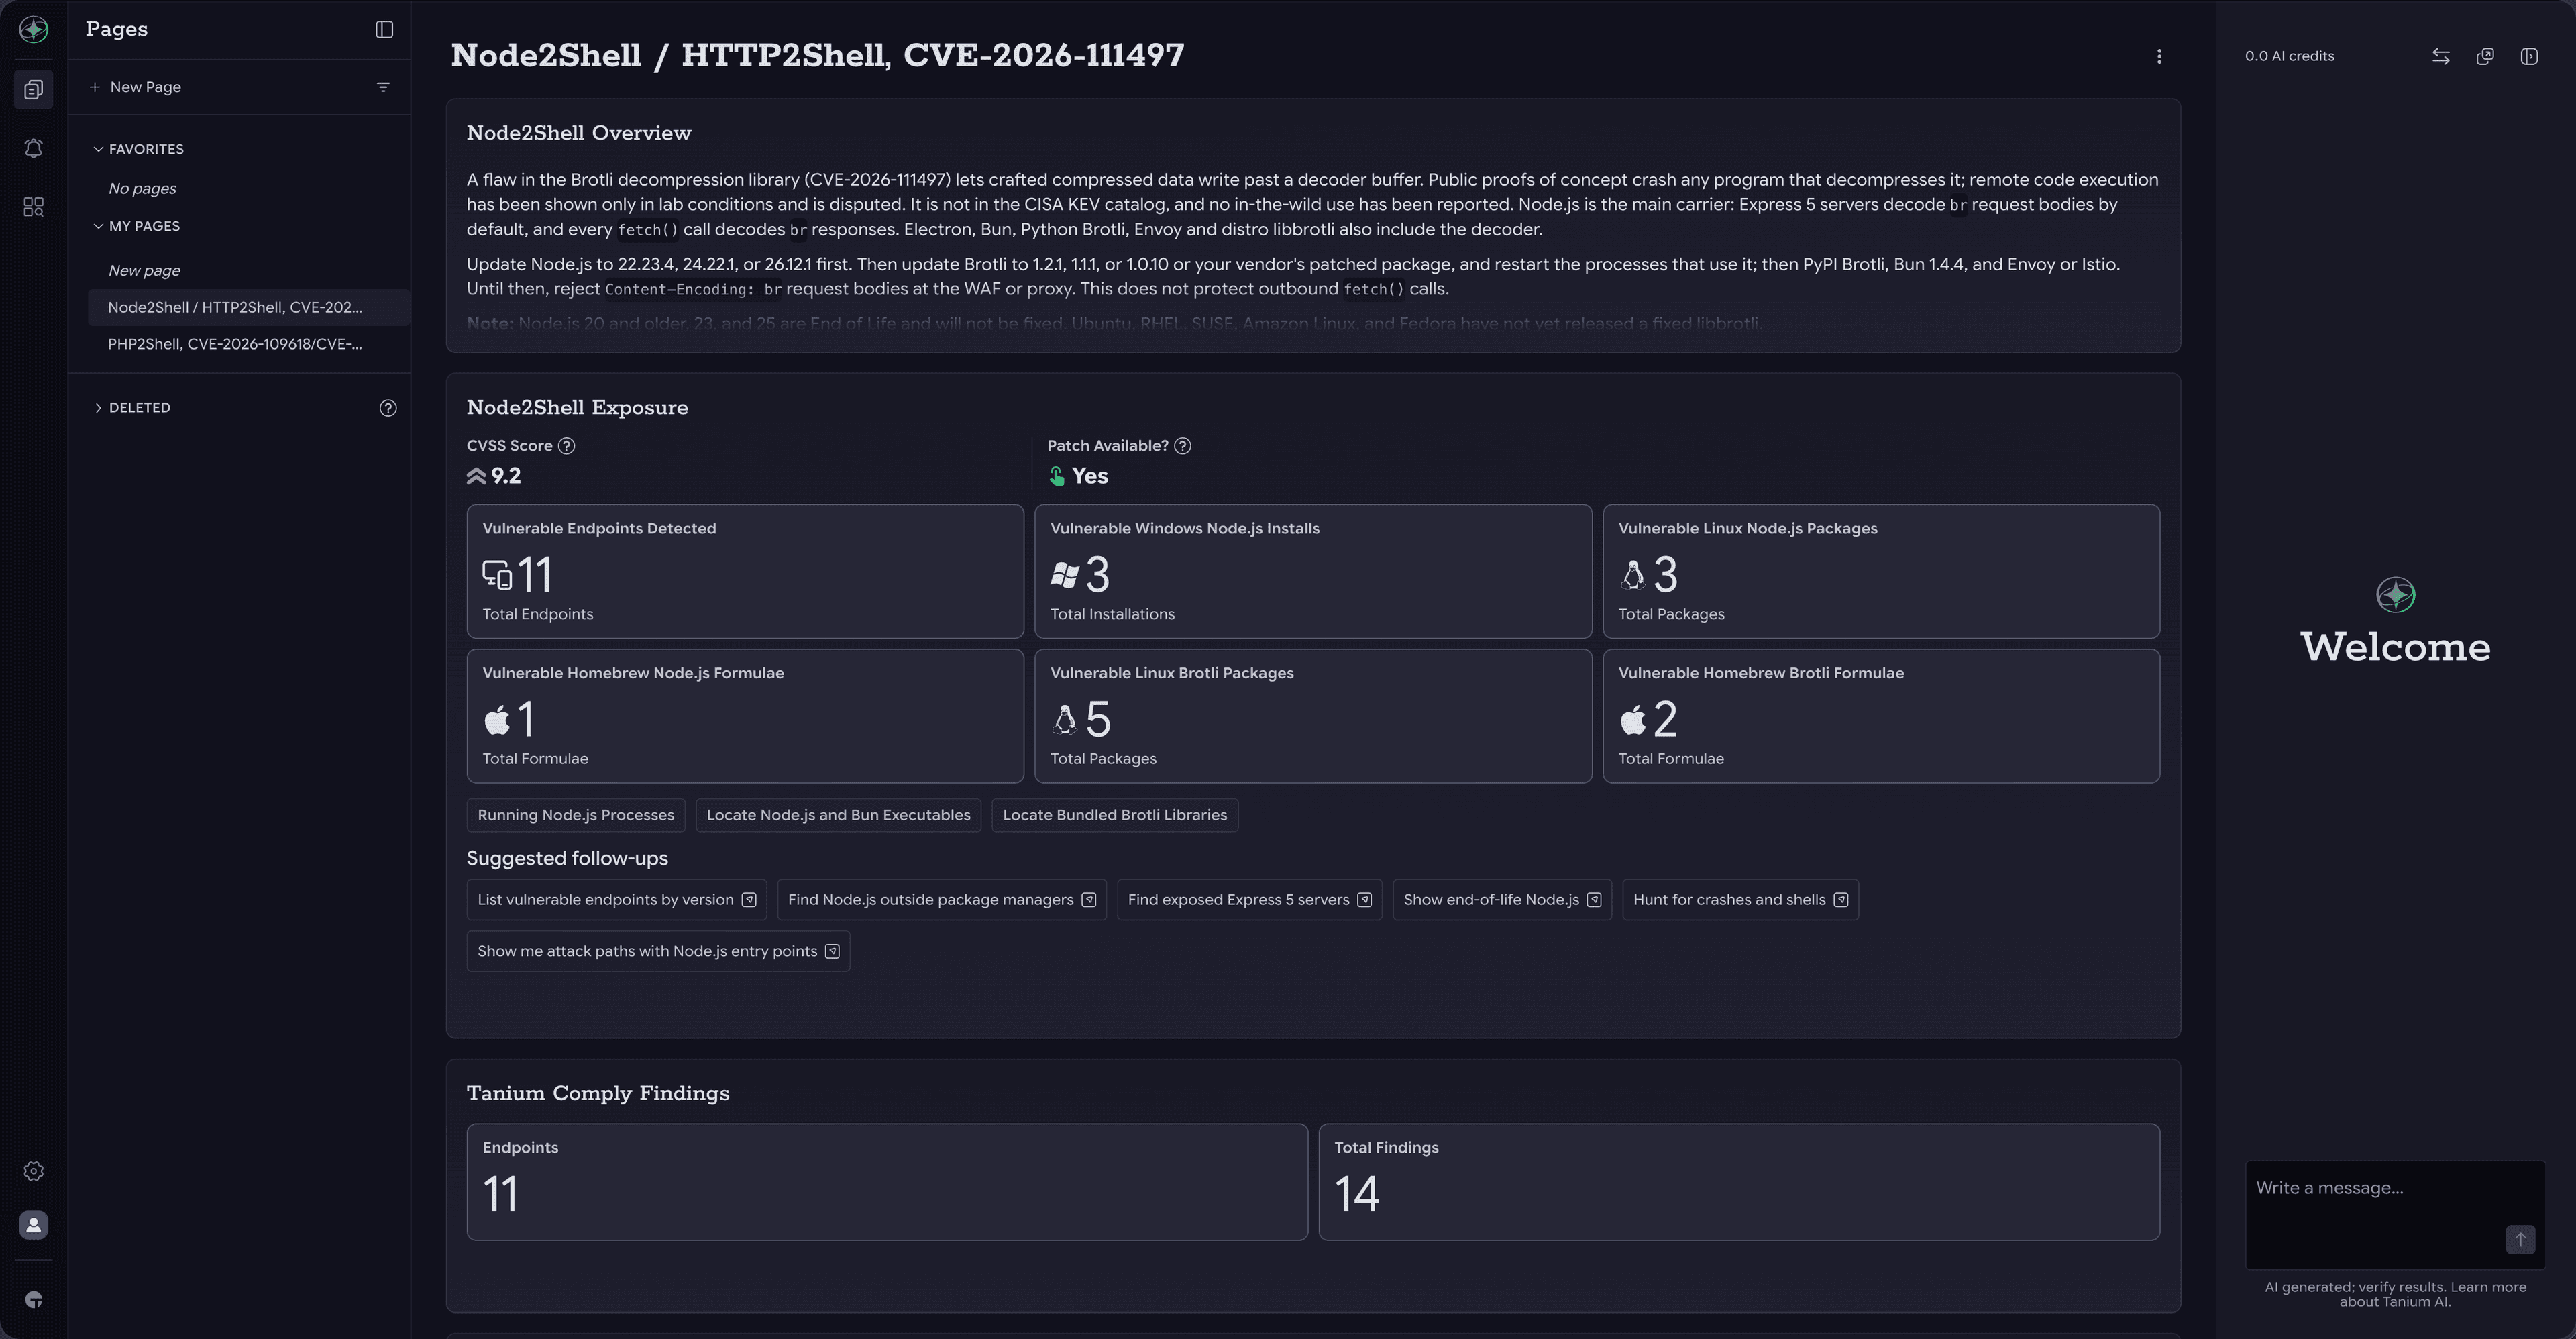
HTTP2Shell: Find and Fix Vulnerable Brotli Copies with Tanium
A critical flaw in Google's Brotli decoder (CVSS 9.2) can let a remote attacker crash or take over apps that decompress Brotli data. Update Node.js, Python Brotli and Bun now.
eMudhra CA Compromise: Find and Fix Your Exposure with Tanium
Private keys for eight eMudhra intermediate CAs can be calculated from their public certificates. Browsers block them once updated; most other software needs a trust store update.
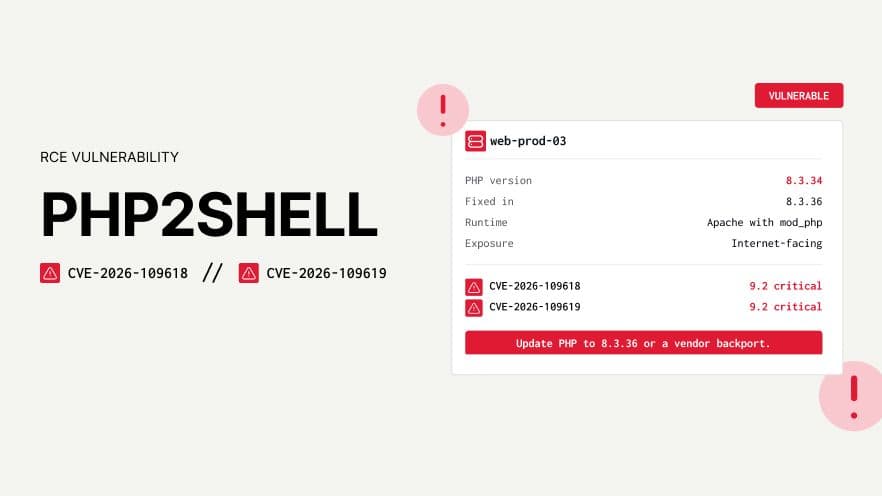
PHP2Shell: Responding to CVE-2026-109618 and CVE-2026-109619
Two critical flaws in PHP core (CVSS 9.2) let an unauthenticated attacker run code with a crafted web request. Patch to 8.5.12, 8.4.27, 8.3.36 or 8.2.35 now.
AI Compute Just Became an Endpoint Problem
This means the supercomputer is becoming a workstation, and the workstation is becoming something IT has never had to manage before.
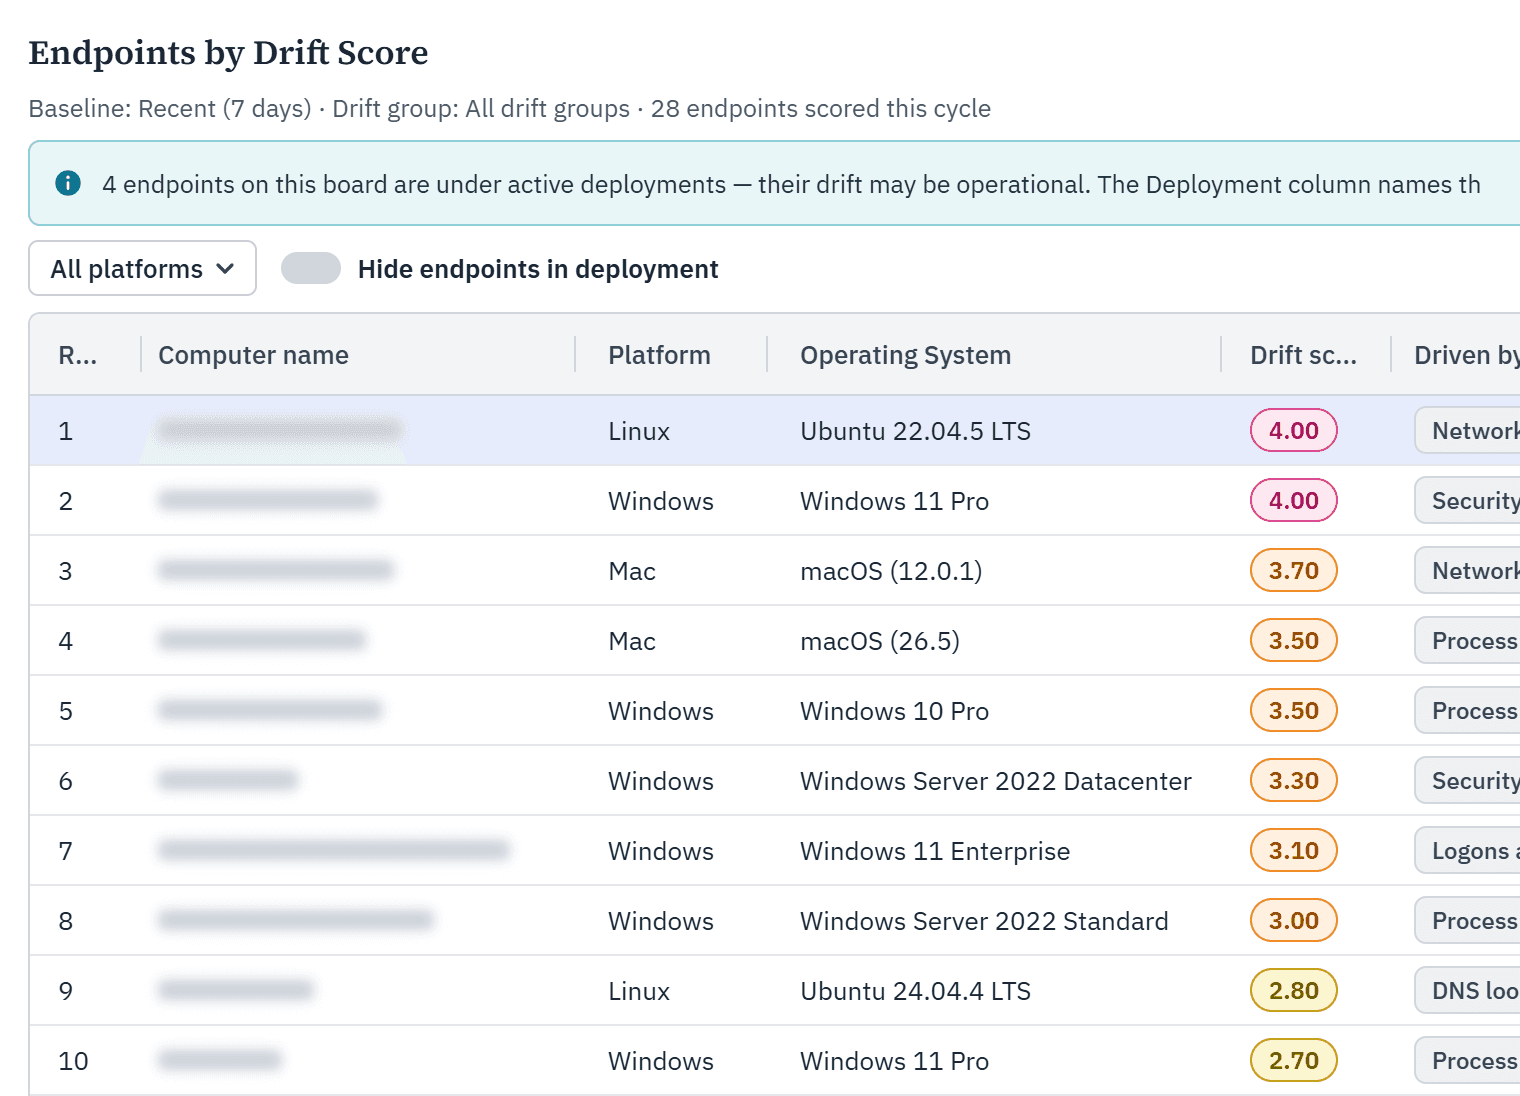
Notice when a machine stops acting like itself: introducing Endpoint Drift
Attackers using stolen logins and your own admin tools won't trigger a single rule — Endpoint Drift notices when a machine stops acting like itself anyway.
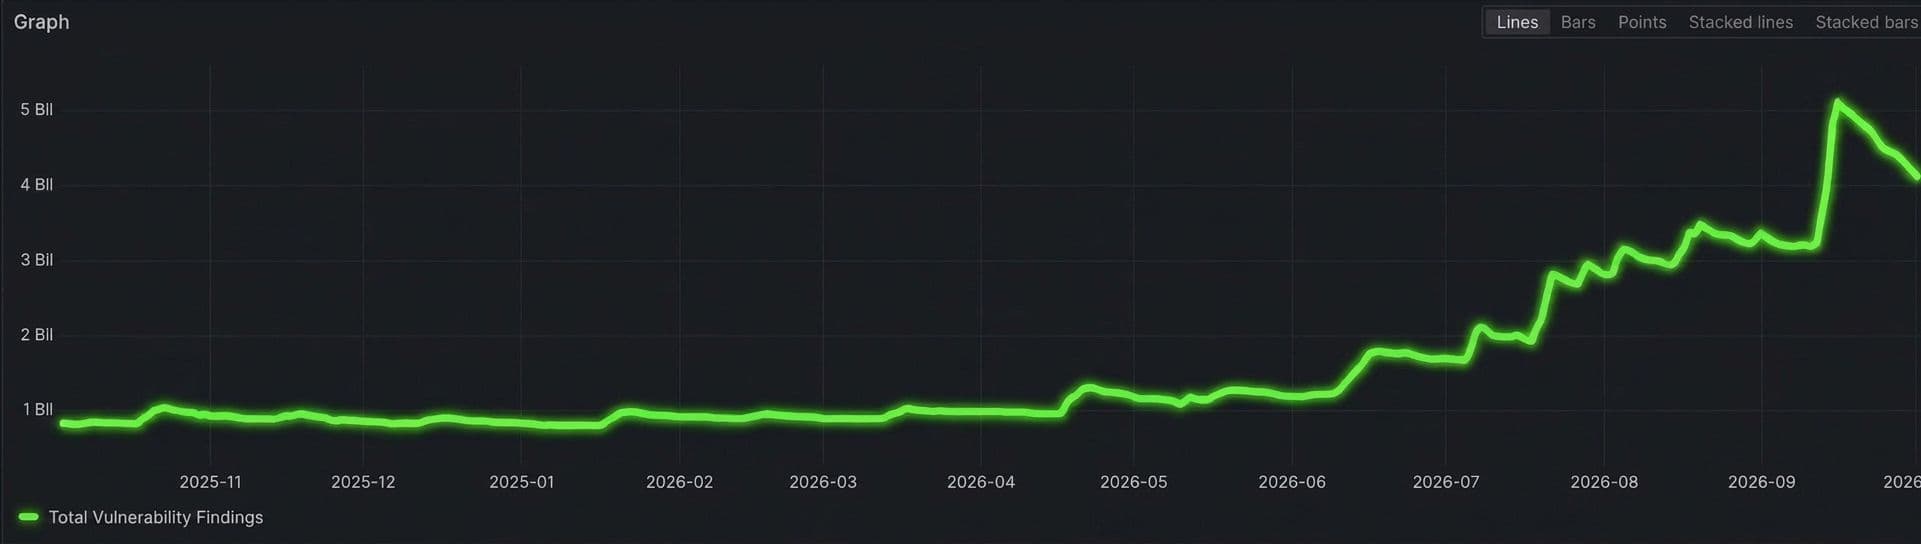
AI Is Accelerating Vulnerability Discovery. Tanium Helps You Keep Up.
Daily vulnerability findings across Tanium customer environments jumped from around 1 billion before mid-June 2026 to as high as 6 billion in September. Here is what is driving the surge and how to keep up.
AI is Accelerating Your Environment. Our Connector Keeps Up: The Next Evolution of the Service Graph Connector for Tanium & ServiceNow
Service Graph Connector for Tanium Atlas, now generally available in the ServiceNow Store, uses delta sync to keep your CMDB current.
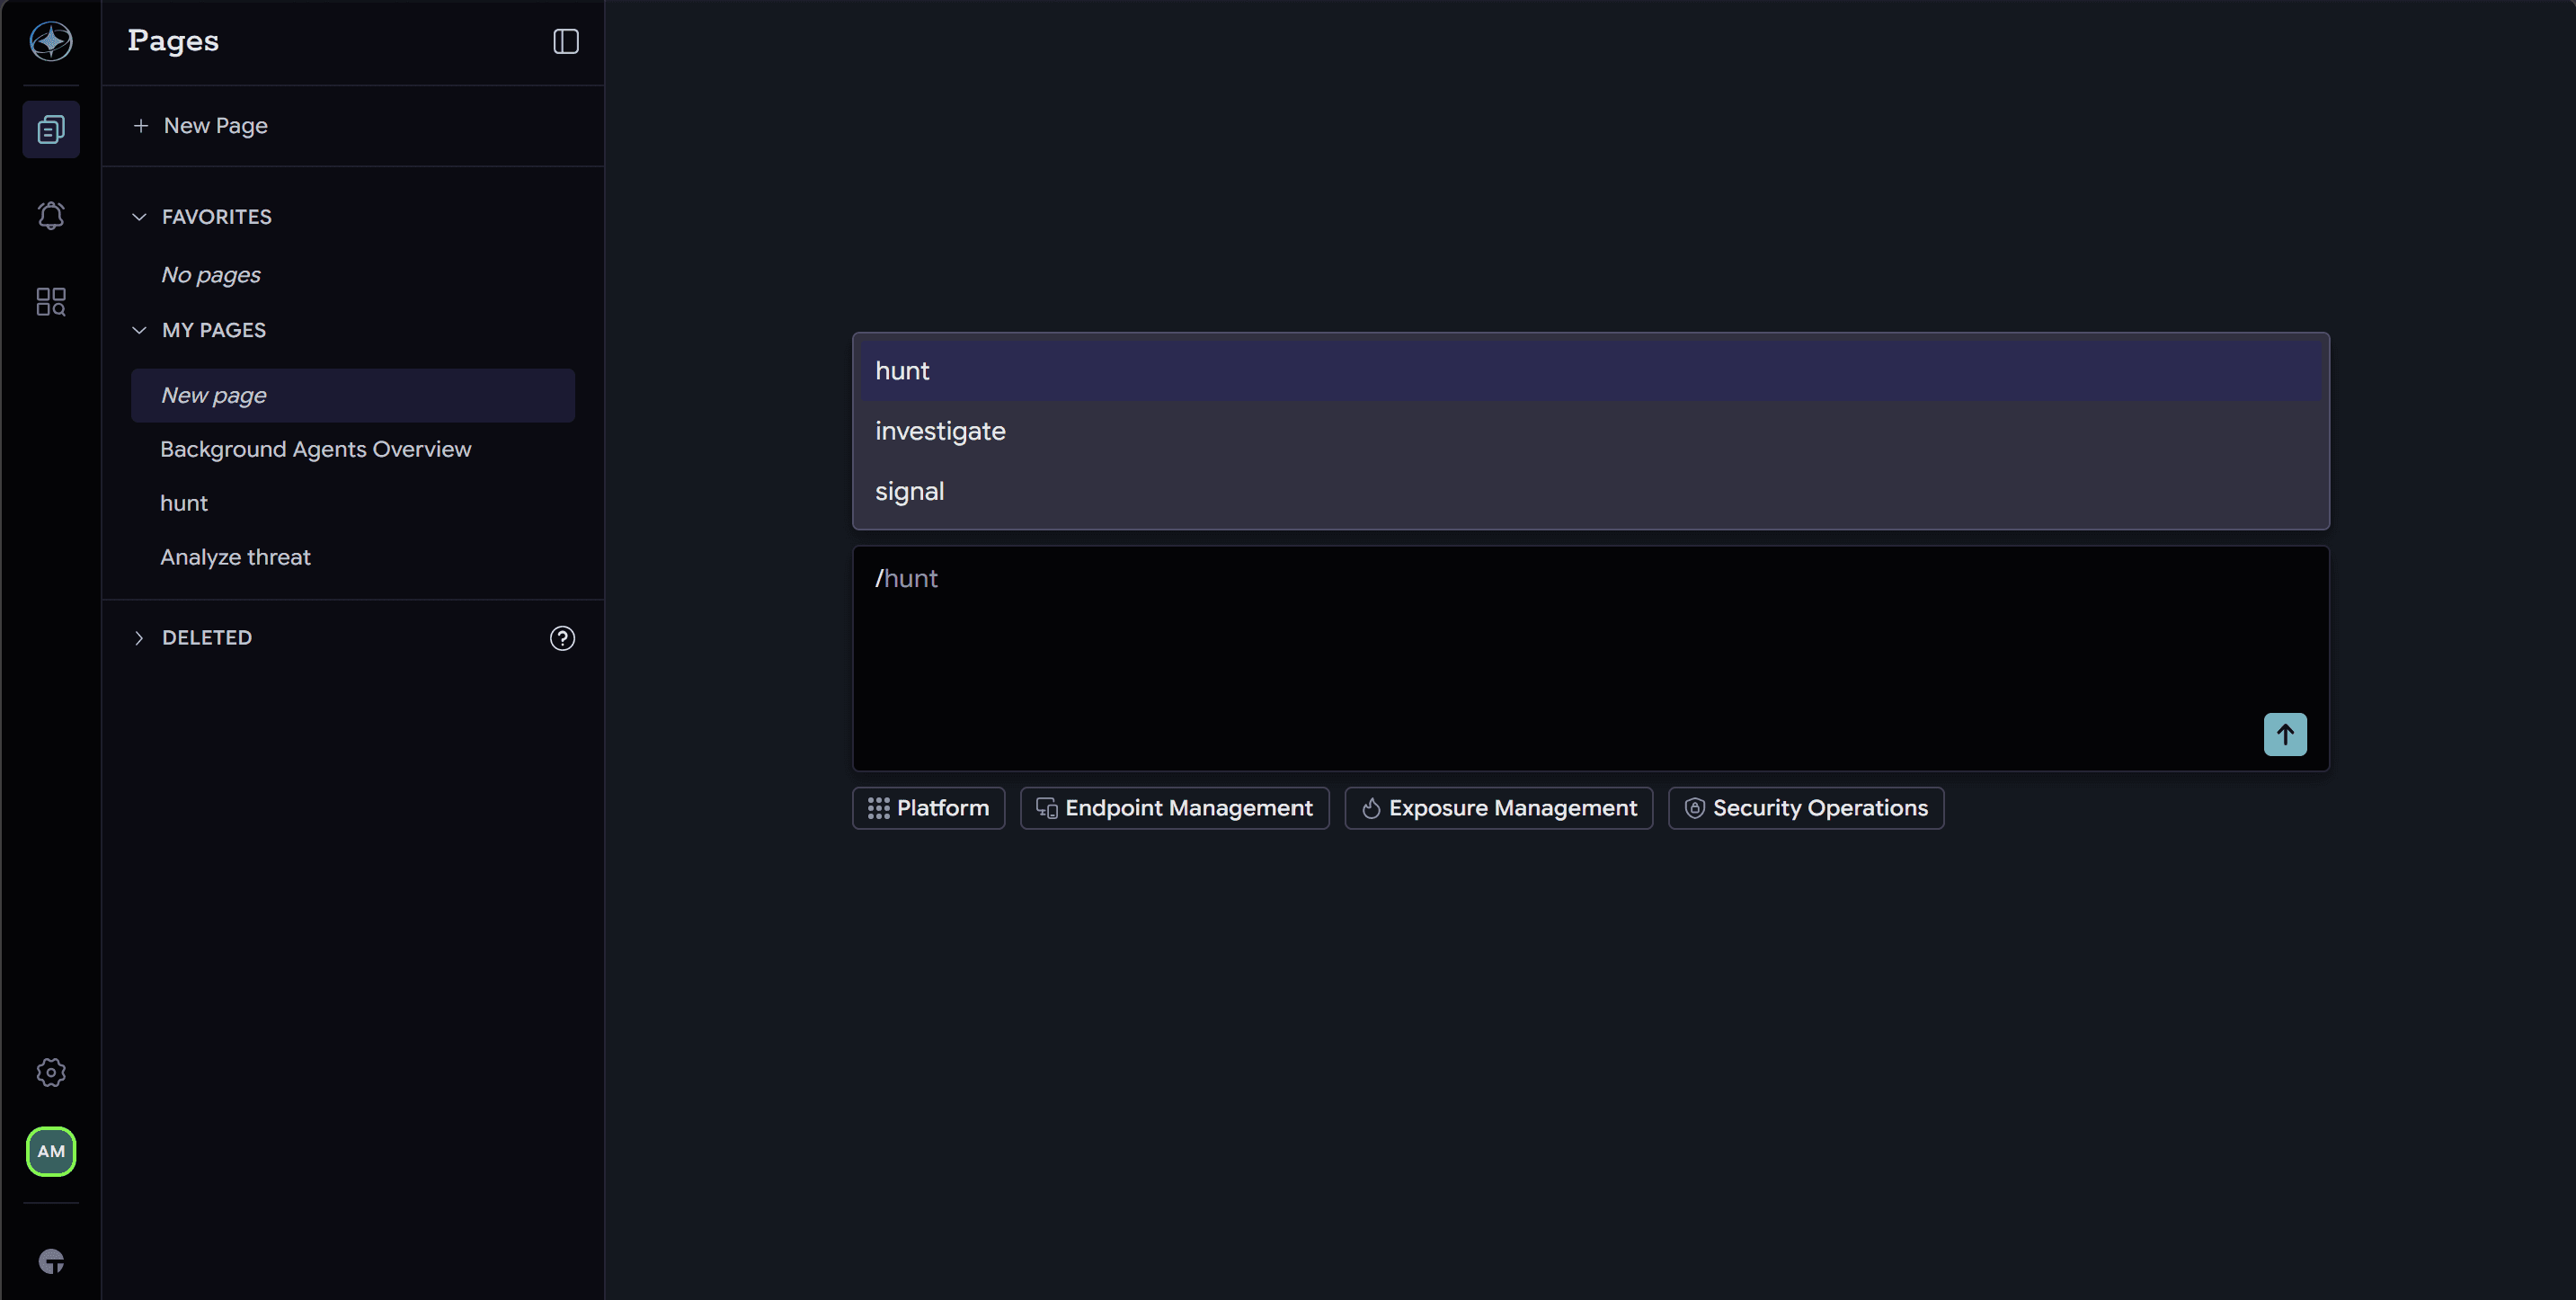
Slash Commands Bring Expert SecOps Workflows to Atlas
With /hunt, /investigate, and /signal, Atlas turns a simple chat interaction into a guided SecOps workflow grounded in live endpoint state.
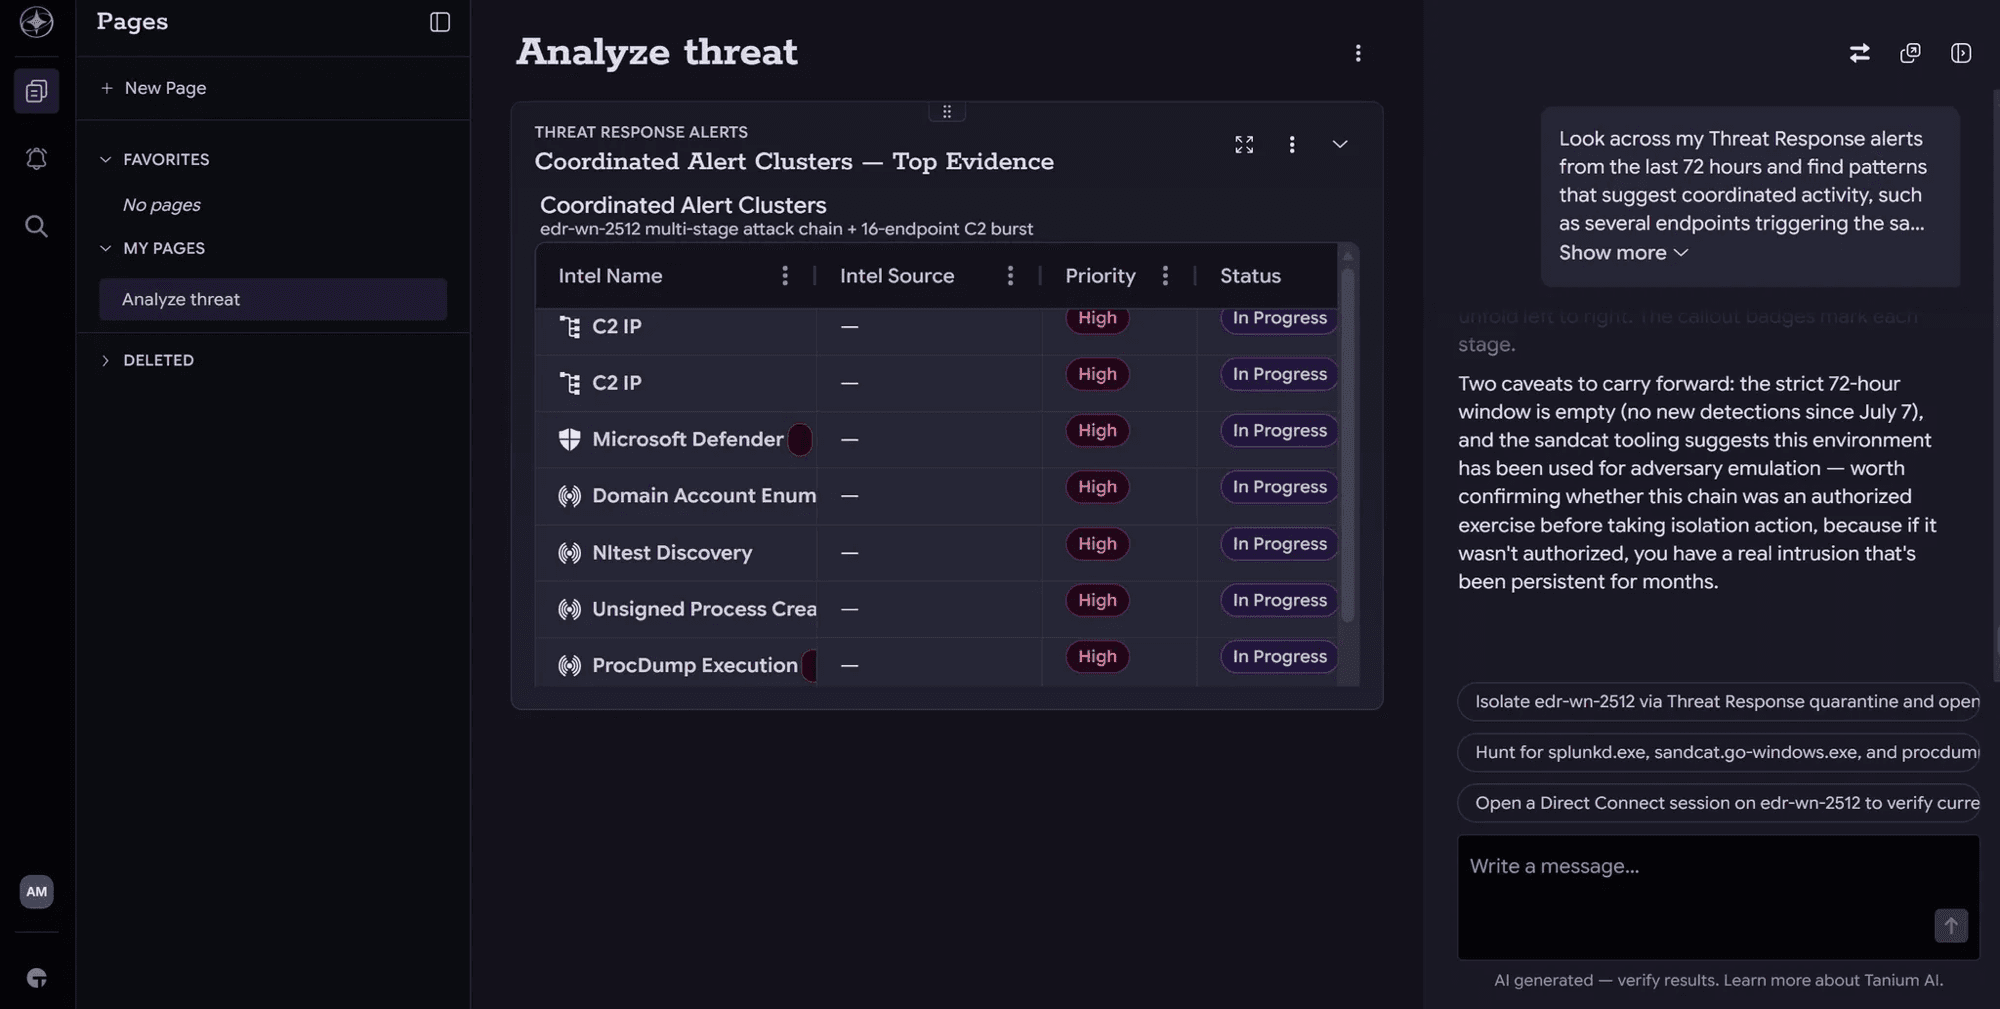
Introducing Agentic SecOps: Live Endpoint Truth for the AI-Driven SOC
Agentic SecOps changes the operating model: with Tanium Atlas, security teams can direct work in natural language, reason over live endpoint data, and keep humans in control.
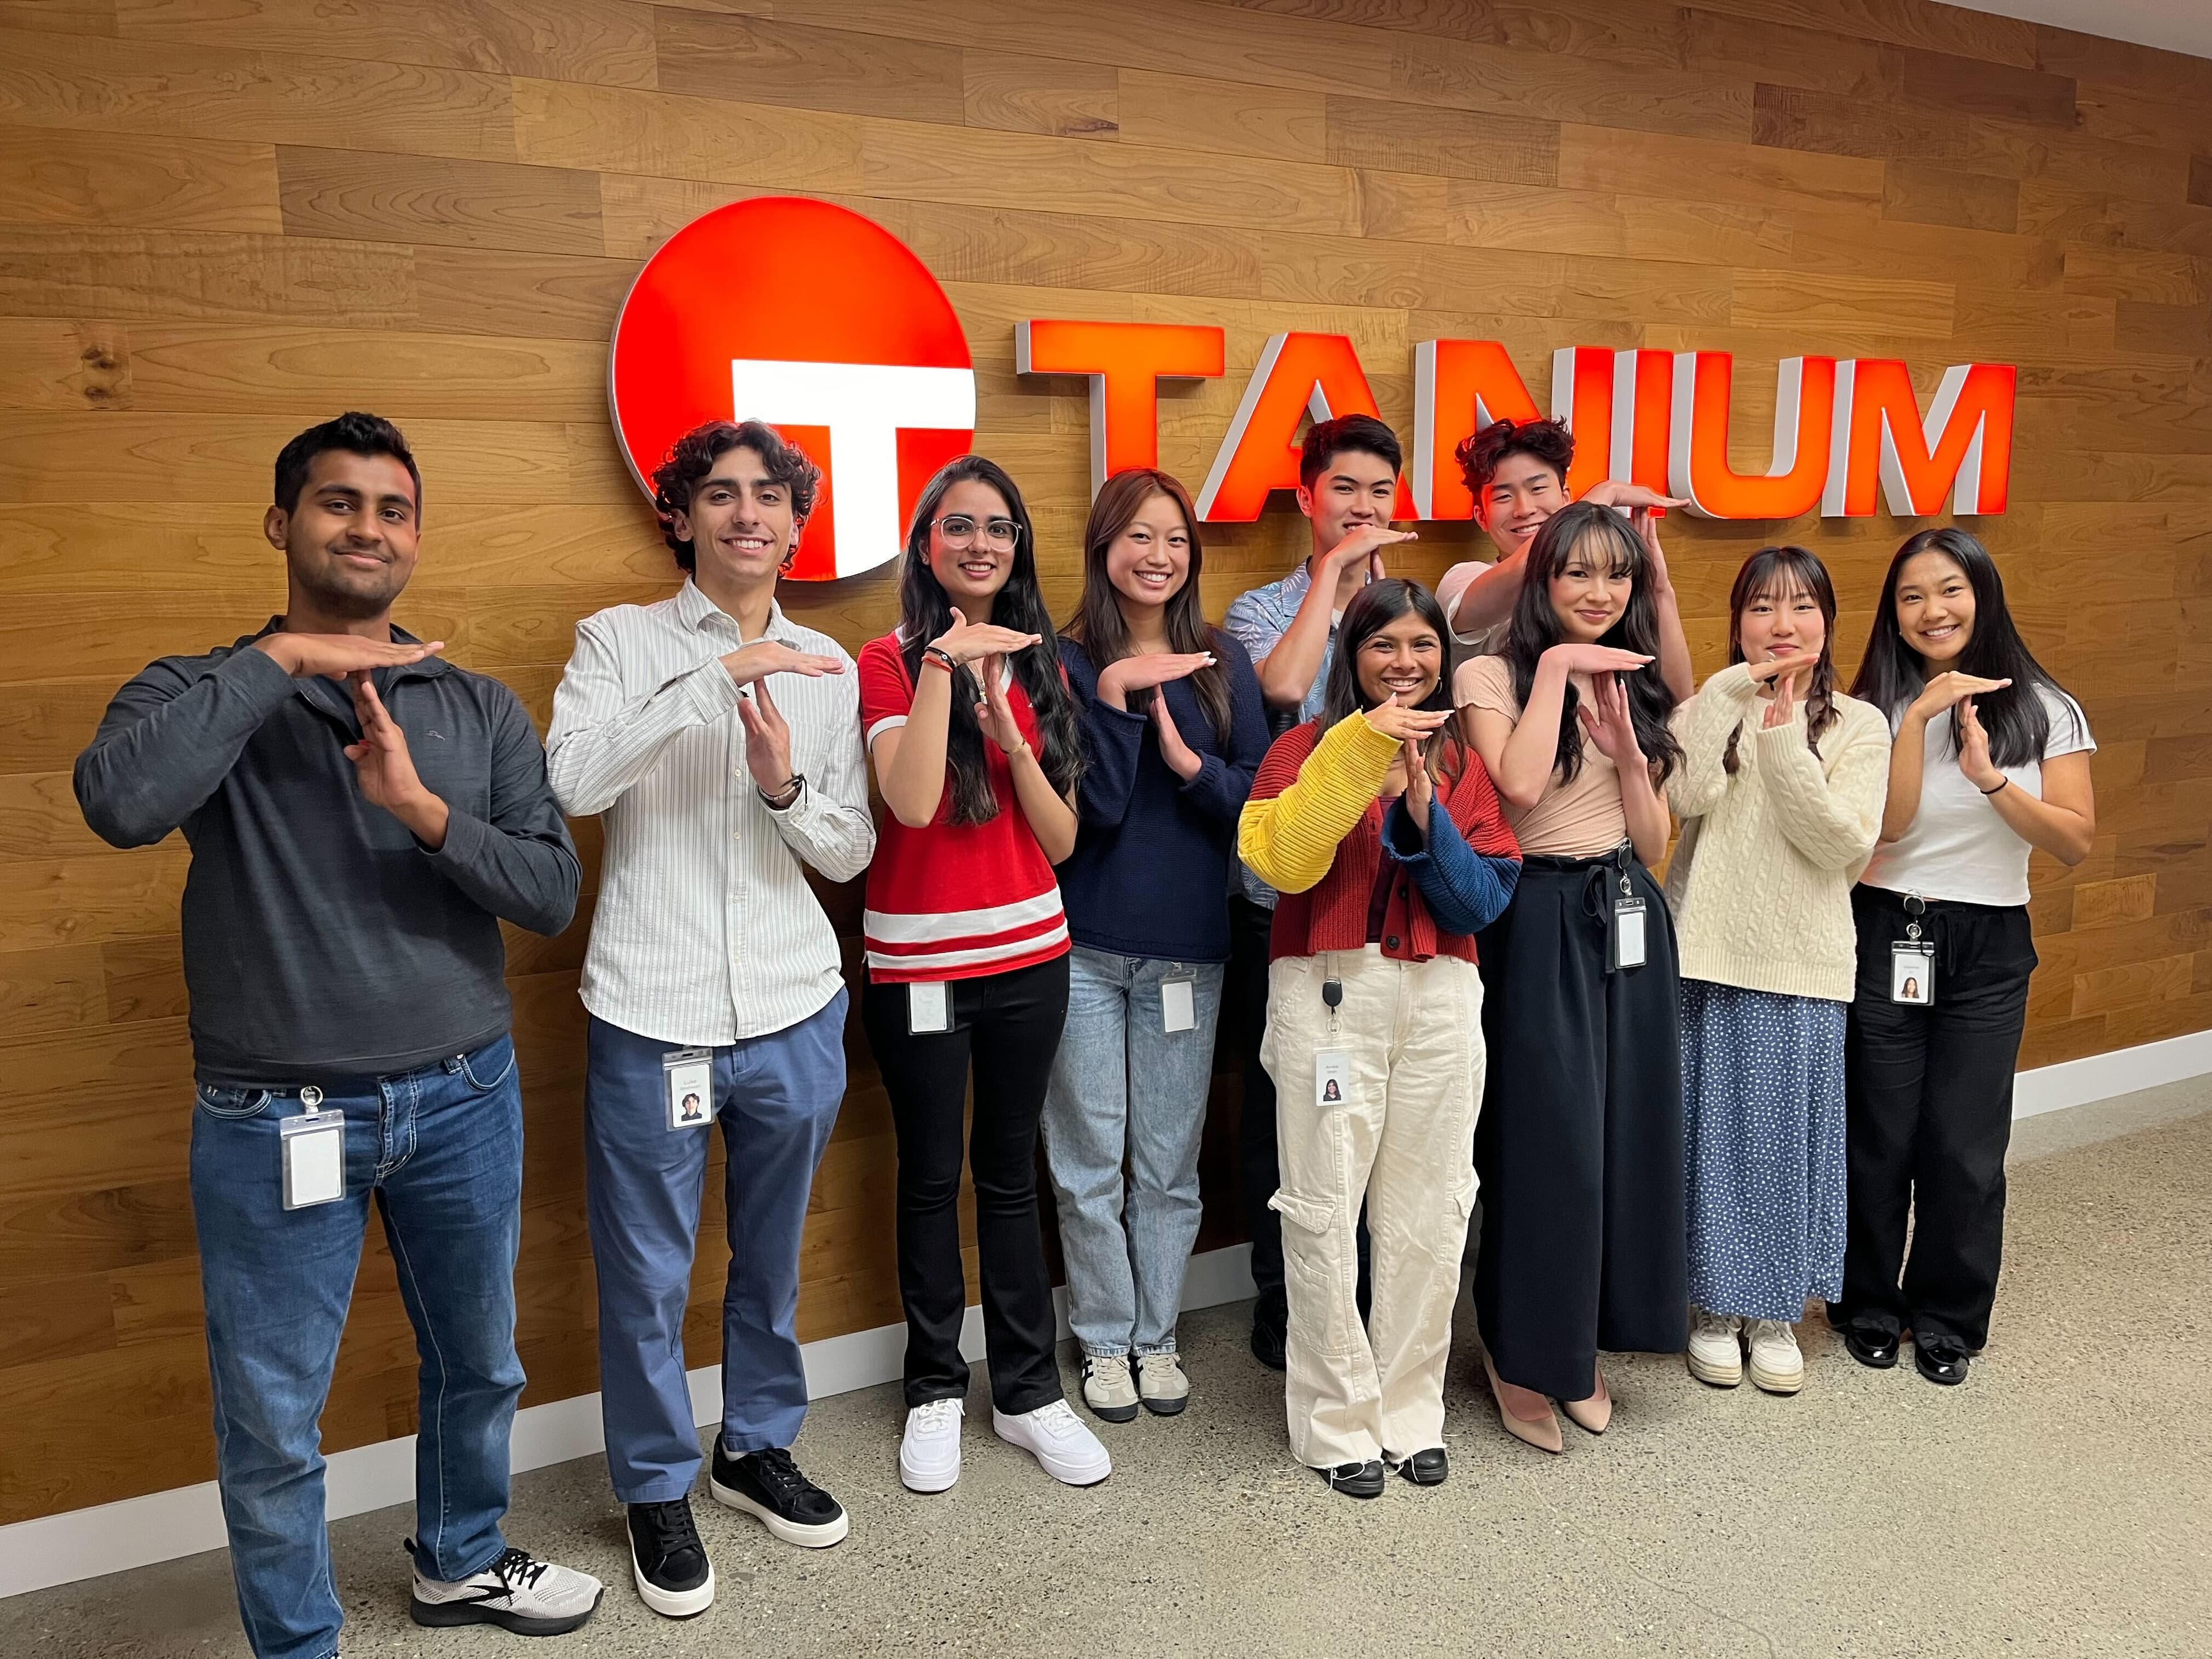
Tanium’s Summer Intern Program: A Launch Pad to Leadership in Cybersecurity
A look at Tanium’s leading summer internship program – and why it’s a great option for students and professionals entering cybersecurity.
Tanium Atlas: One operator. The full weight of the platform.
Tanium Atlas is generally available to every commercial and U.S. Government cloud customer. Here's what changes for the operators doing the work in an AI threat landscape, and why I wanted to write this one myself.
See the full attack surface. Act on what actually matters.
CVE volumes are climbing, AI-discovered threats are multiplying, and visibility across the full attack surface remains fragmented. Bolt-on solutions and manual handoffs simply can't keep pace. Organizations who are getting ahead share one thing in common: they've replaced fragmented workflows with AI-powered prioritization and autonomous remediation across a unified view of both internal and external risk.