TANIUM SECURITY OPERATIONS
The Reactive SOC Ends Here
Attackers move at machine speed now, and your security team should too. See what's happening on every endpoint in real time, act on it instantly, and hunt down what's still hiding before it becomes a headline.

BUILD THE SELF-DRIVING SOC
Modernize the SOC. Move at machine-speed.

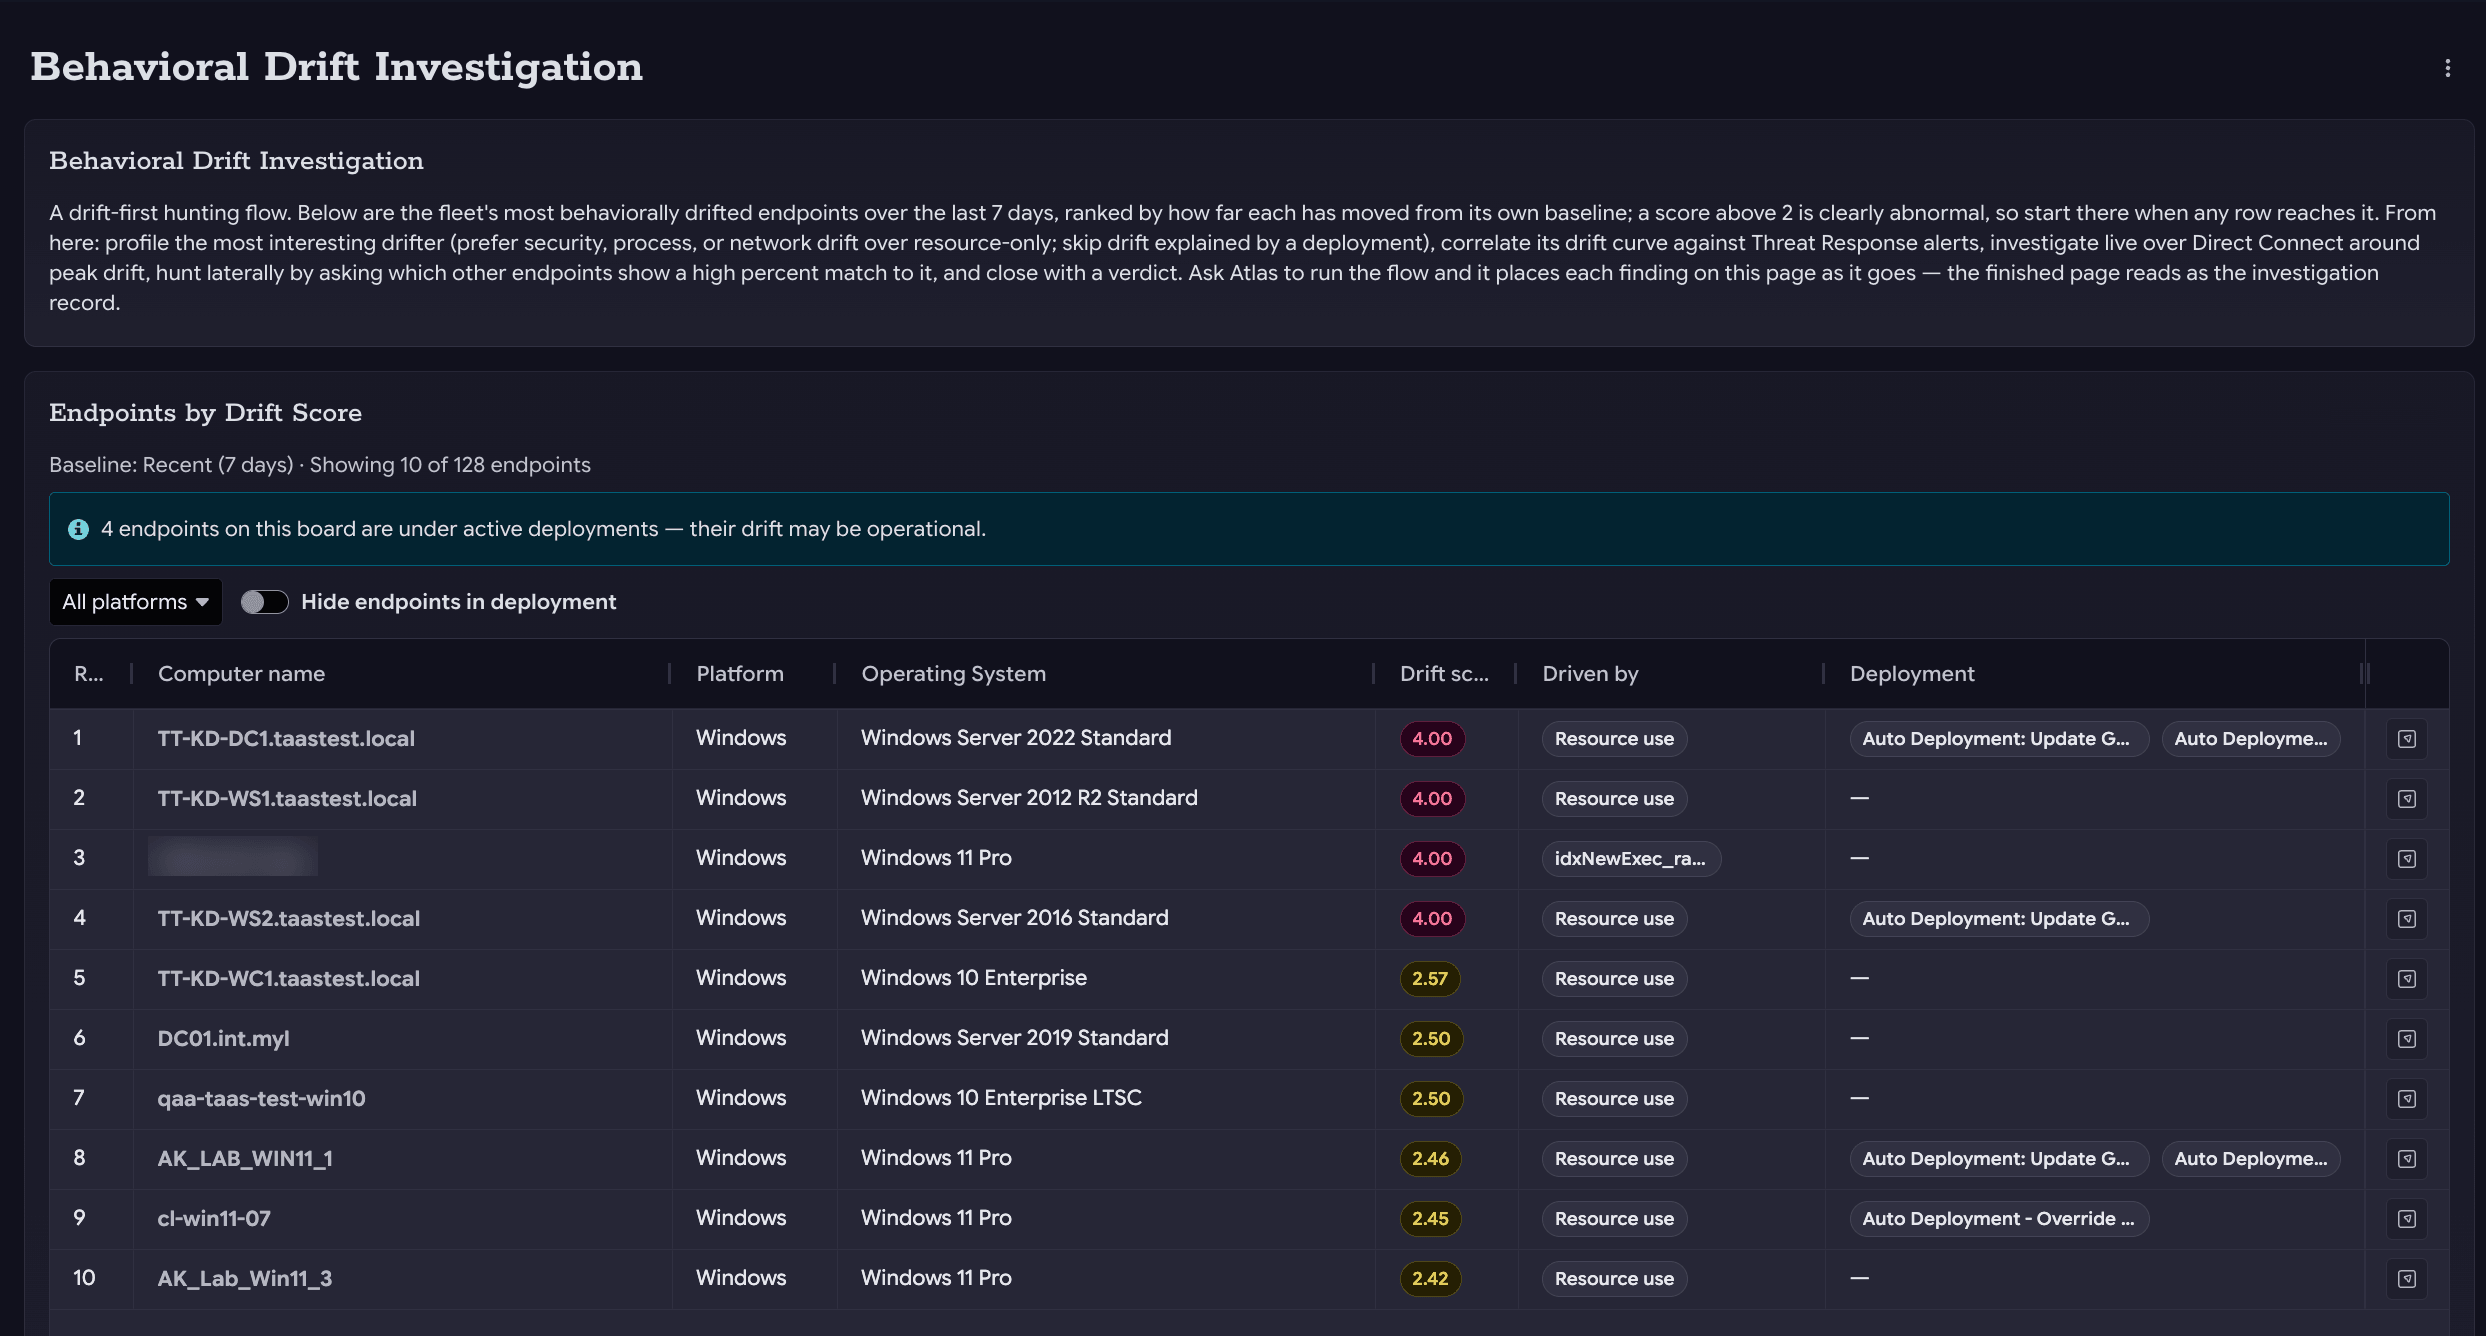
Know normal. Catch what isn't.
Query any endpoint fleet-wide, live or historical, and baseline normal behavior to catch drift.

From detection to resolution, instantly
Scope incidents in seconds, isolate and remediate endpoints instantly at scale, even when they're offline.

Machine speed, with you in control
Set limits for Atlas, dry-run every response, require approval, and control access by role.

Visibility into AI and agentic infrastructure
Understand the MCP servers, model managers, and AI agents running in your environment.
SECURITY OPERATIONS
Built to Outpace the Attack
Detection, response, and hunting work together on one platform, all running on live data from every endpoint you own.
Detection of Modern Threats
Know what's happening now, not what happened yesterday.
- Catch living-off-the-land attacks and lateral movement hiding in normal activity
- Search your whole fleet live, with historical data and forensics alongside it
- Work the riskiest alerts first, ranked with Google Threat Intelligence
HUNTIQ
Hunt like you have a team of experts. Because you do.
Threat hunting is one of the most valuable things your security team does, and one of the hardest to staff. HuntIQ puts Tanium's own threat hunters inside your environment, working alongside your team to find what automation alone misses.

Know what's real, faster
Tanium's expert hunters work directly in your environment, proving or disproving risk with a disciplined method, so your team acts on real threats instead of guesses.

Fewer false alarms
Tuned intelligence, sharper detection logic, and custom sensors and queries built for your environment cut the noise, so you can focus on the risks that actually hit the business.

Every hunt makes you stronger
HuntIQ learns what normal looks like, flags unusual behavior across your whole estate, and feeds what it finds back to your engineering team, so every hunt starts smarter than the last.
Latest in Security Operations
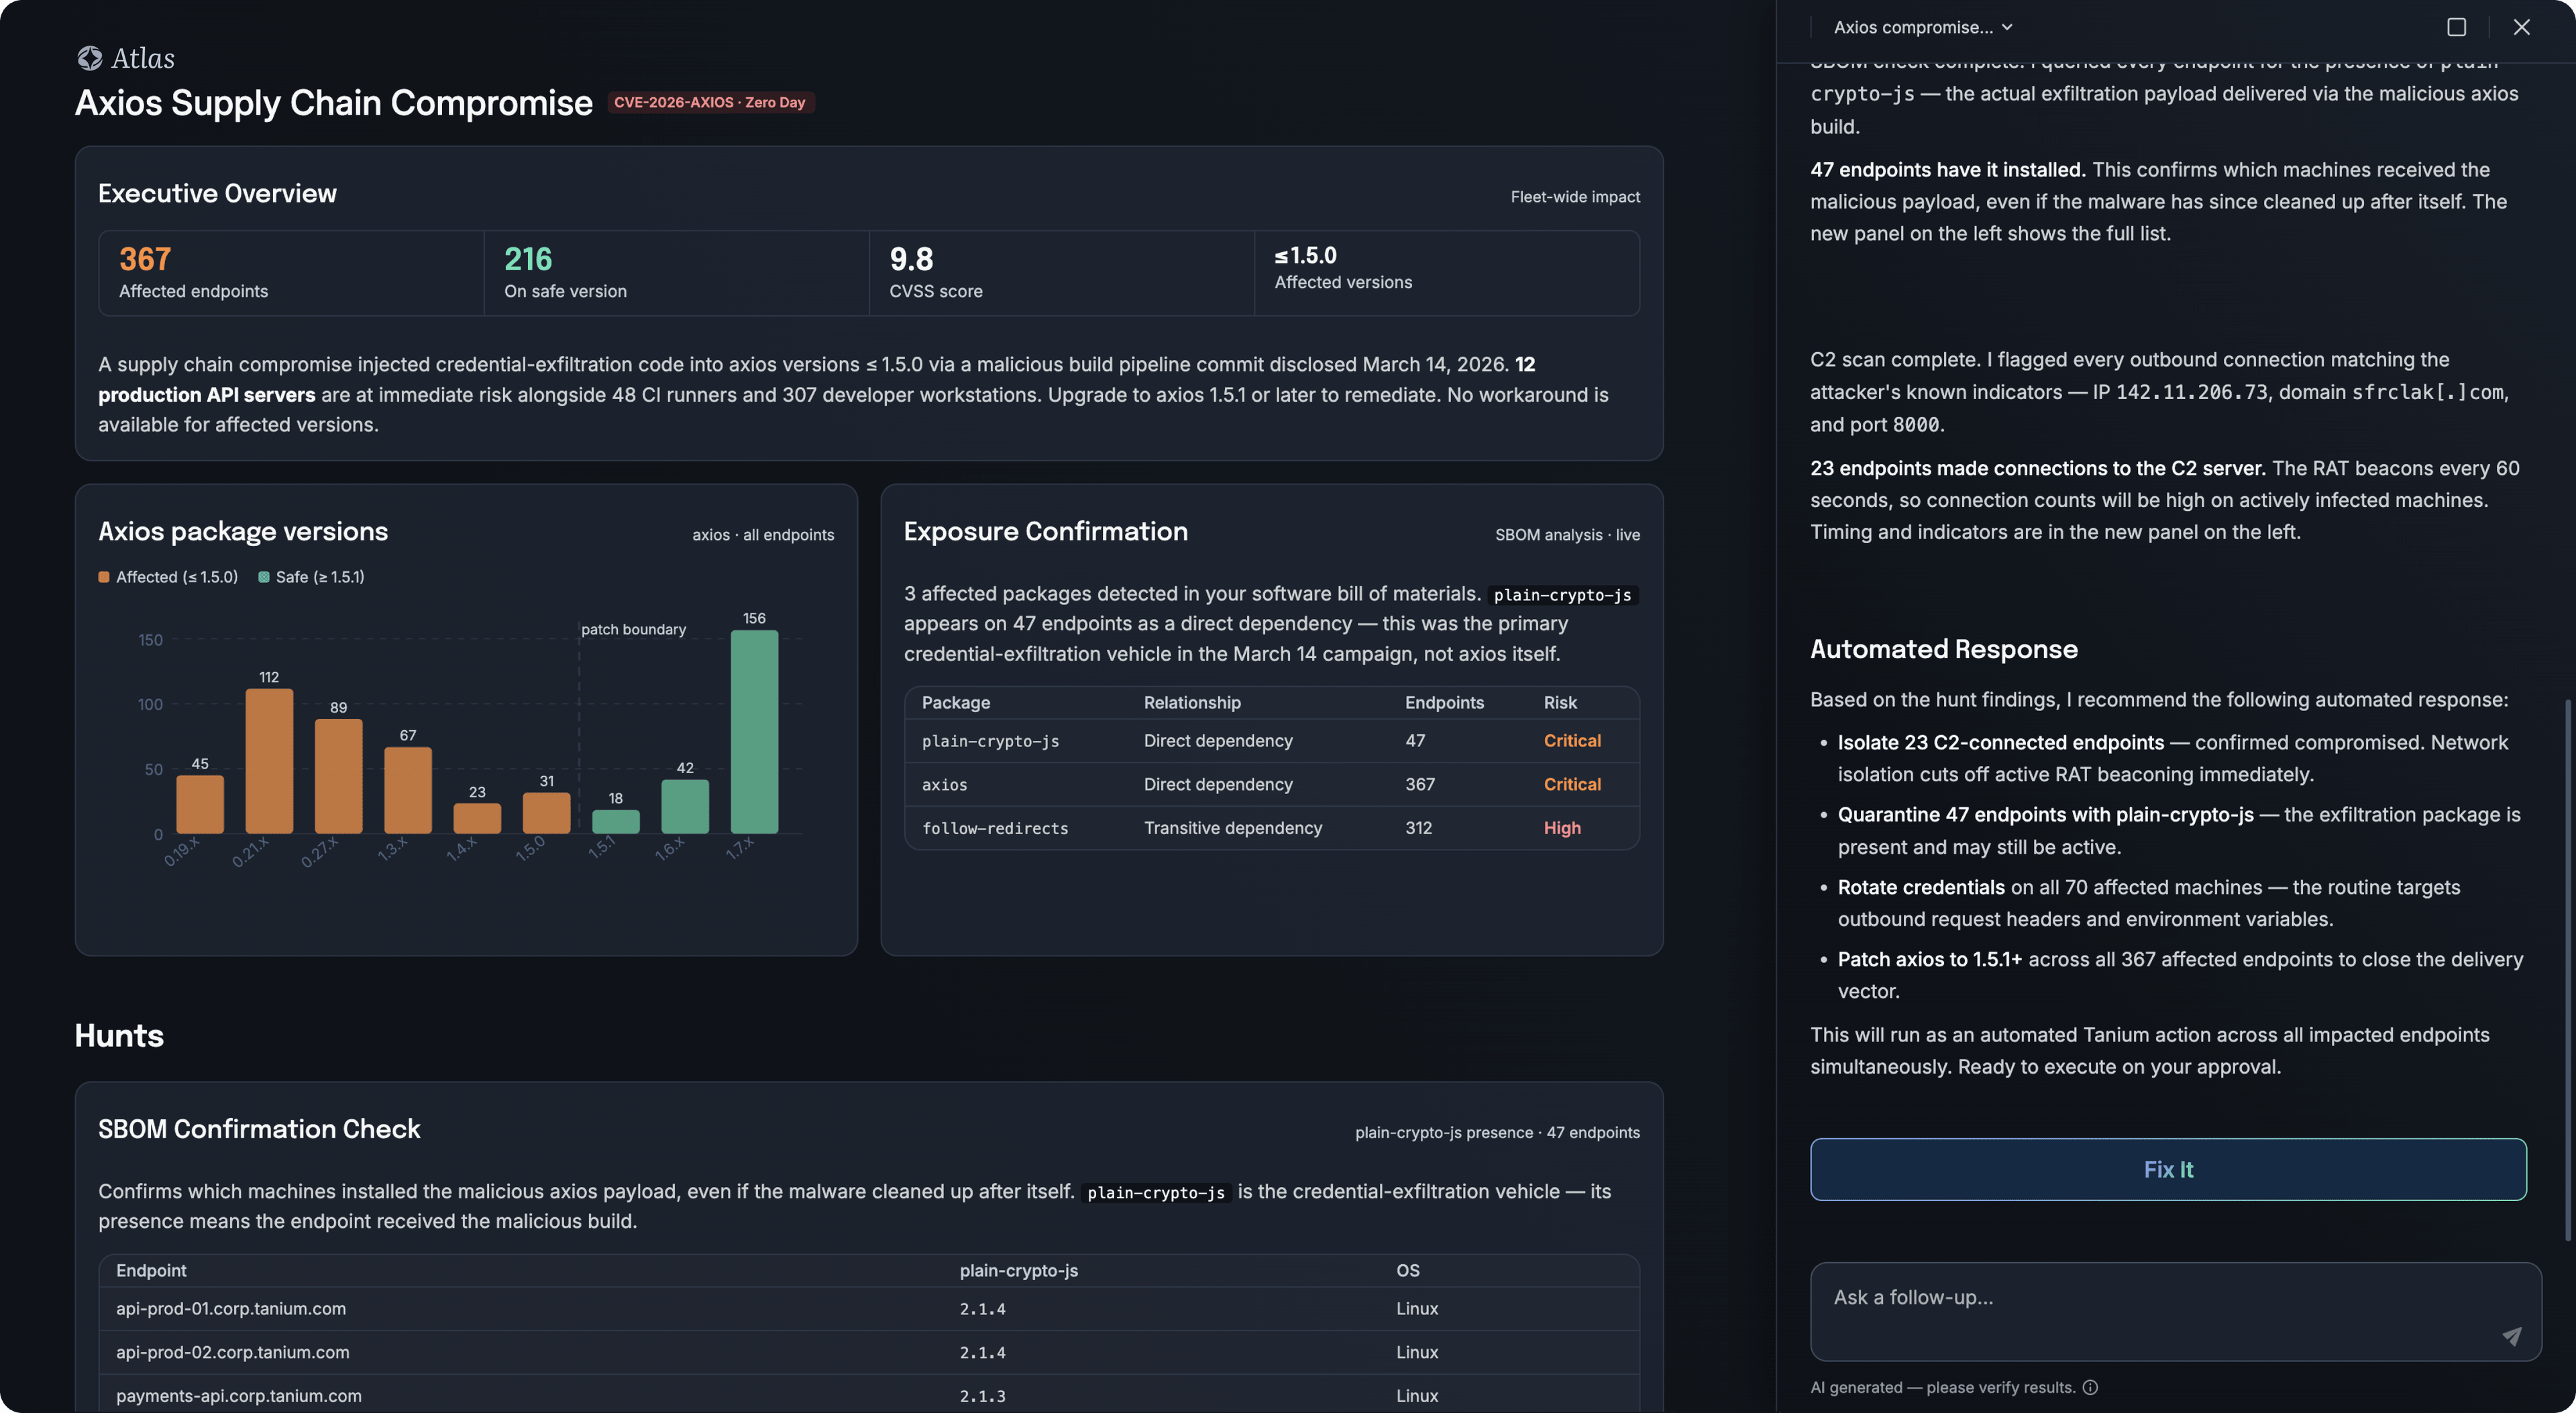
From Mythos to Machine-Speed Defense
Frontier AI has shrunk the time from discovery to exploit to hours. See how Tanium Atlas takes one operator from question to resolution, with human approval built in.
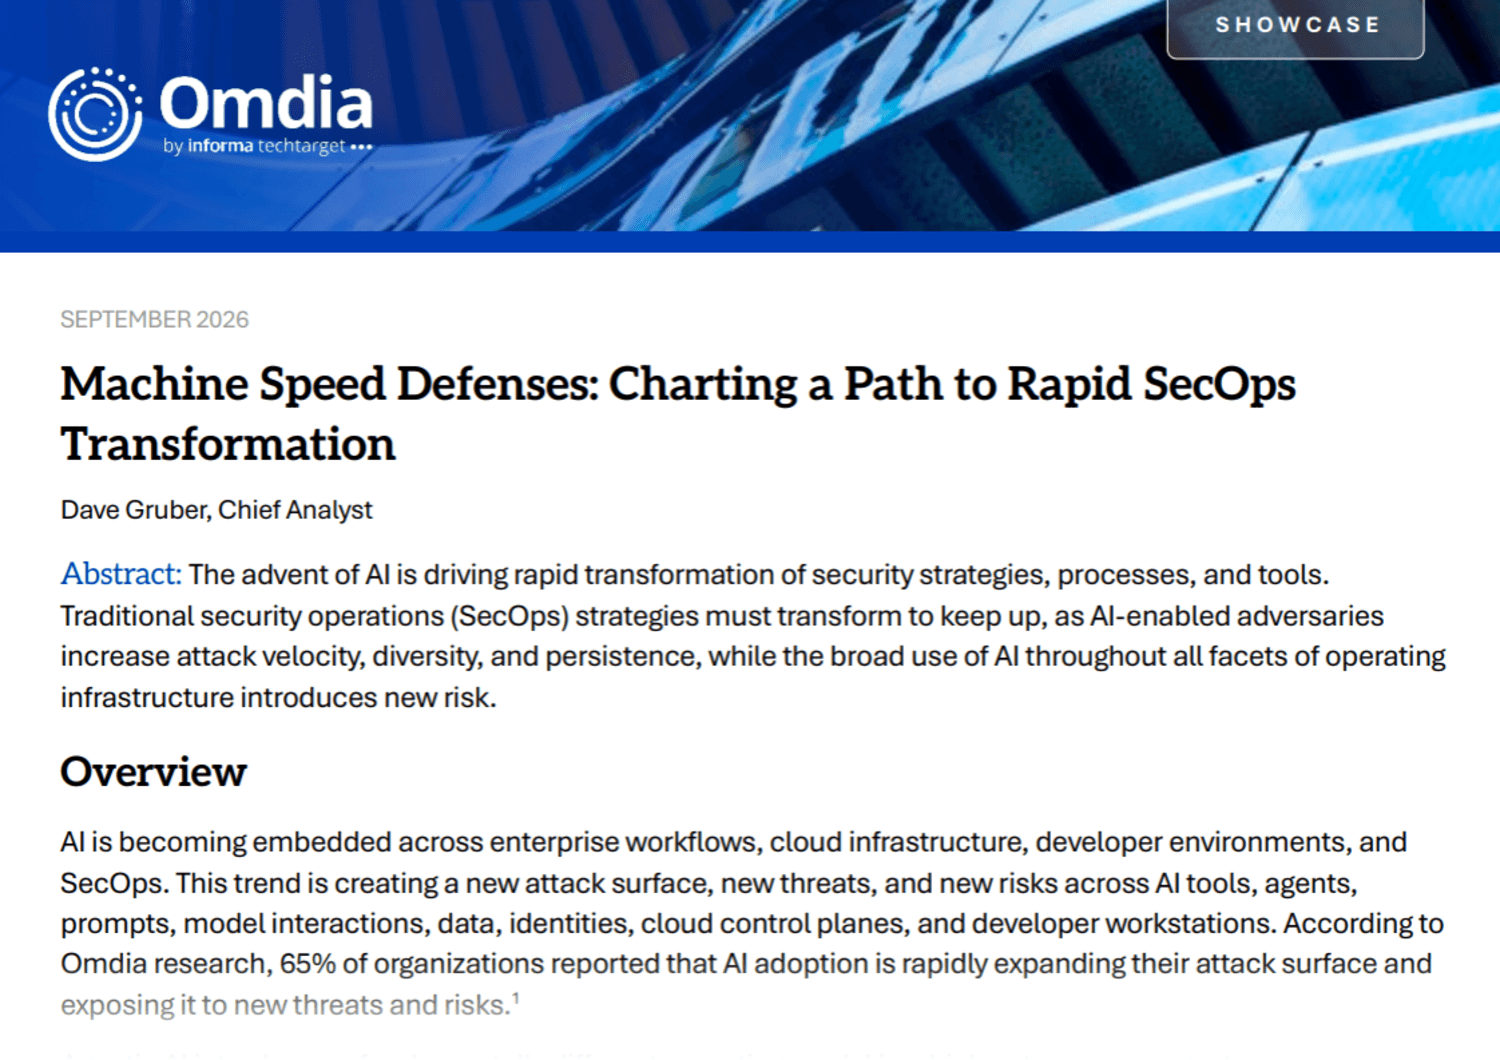
Machine Speed Defenses: Charting a Path to Rapid SecOps Transformation
Omdia examines how AI is reshaping security operations, and what SecOps teams need to keep pace with machine-speed threats.
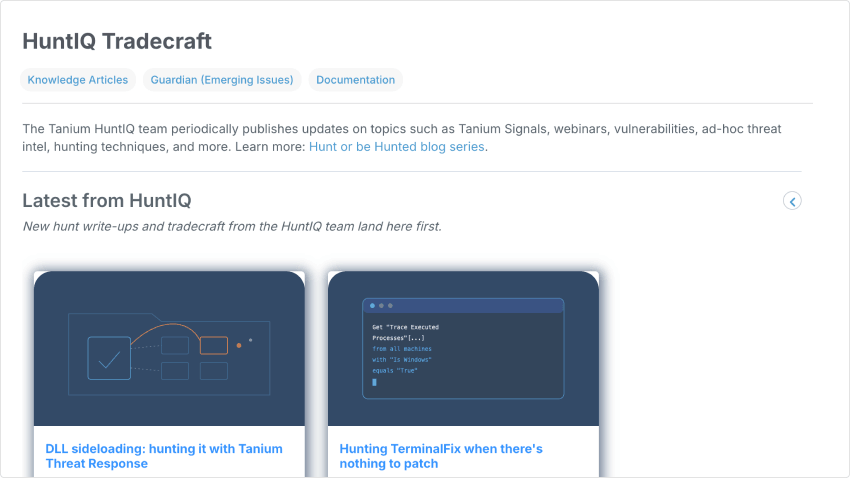
Hunter Wins: HuntIQ Tradecraft is your new hunt library
The Hunt or be Hunted series tells the hunt stories. HuntIQ Tradecraft, now live on the Tanium Resource Center, gives you the playbooks to run them yourself.
CUSTOMER TESTIMONIAL
“Automation Endpoint Management represents the most significant advancement in endpoint management in over a decade.”
THE TANIUM PLATFORM
Security and IT, working from the same data.
Stop paying for tools that don't talk to each other. Security Operations runs on the same platform as your endpoint and exposure management, so the team that finds a problem and the team that fixes it work from the same live data.
Use left and right arrow keys to navigate through the cards.
FAQ
Questions, answered.
Common questions about how Tanium helps security teams detect, respond, and hunt.
BE READY NOW
Ready to end the reactive SOC?
Bring your toughest question. We’ll answer it live, across every endpoint, in seconds.