Topic
Threat Intelligence
Hunt or be Hunted: HuntIQ Hunters Take on php2shell
Learn how Tanium put a fleet-wide PHP inventory in every Tanium Cloud tenant about eight hours after PHP shipped its php2shell fix.
Hunt or be Hunted: The Crash That Gives HTTP2Shell Away
Learn how Tanium turned a bug hidden inside other software into a fleet-wide answer, a tested Tanium Atlas hunt and lab-proven detection guidance within a day of the flaw's scope widening.
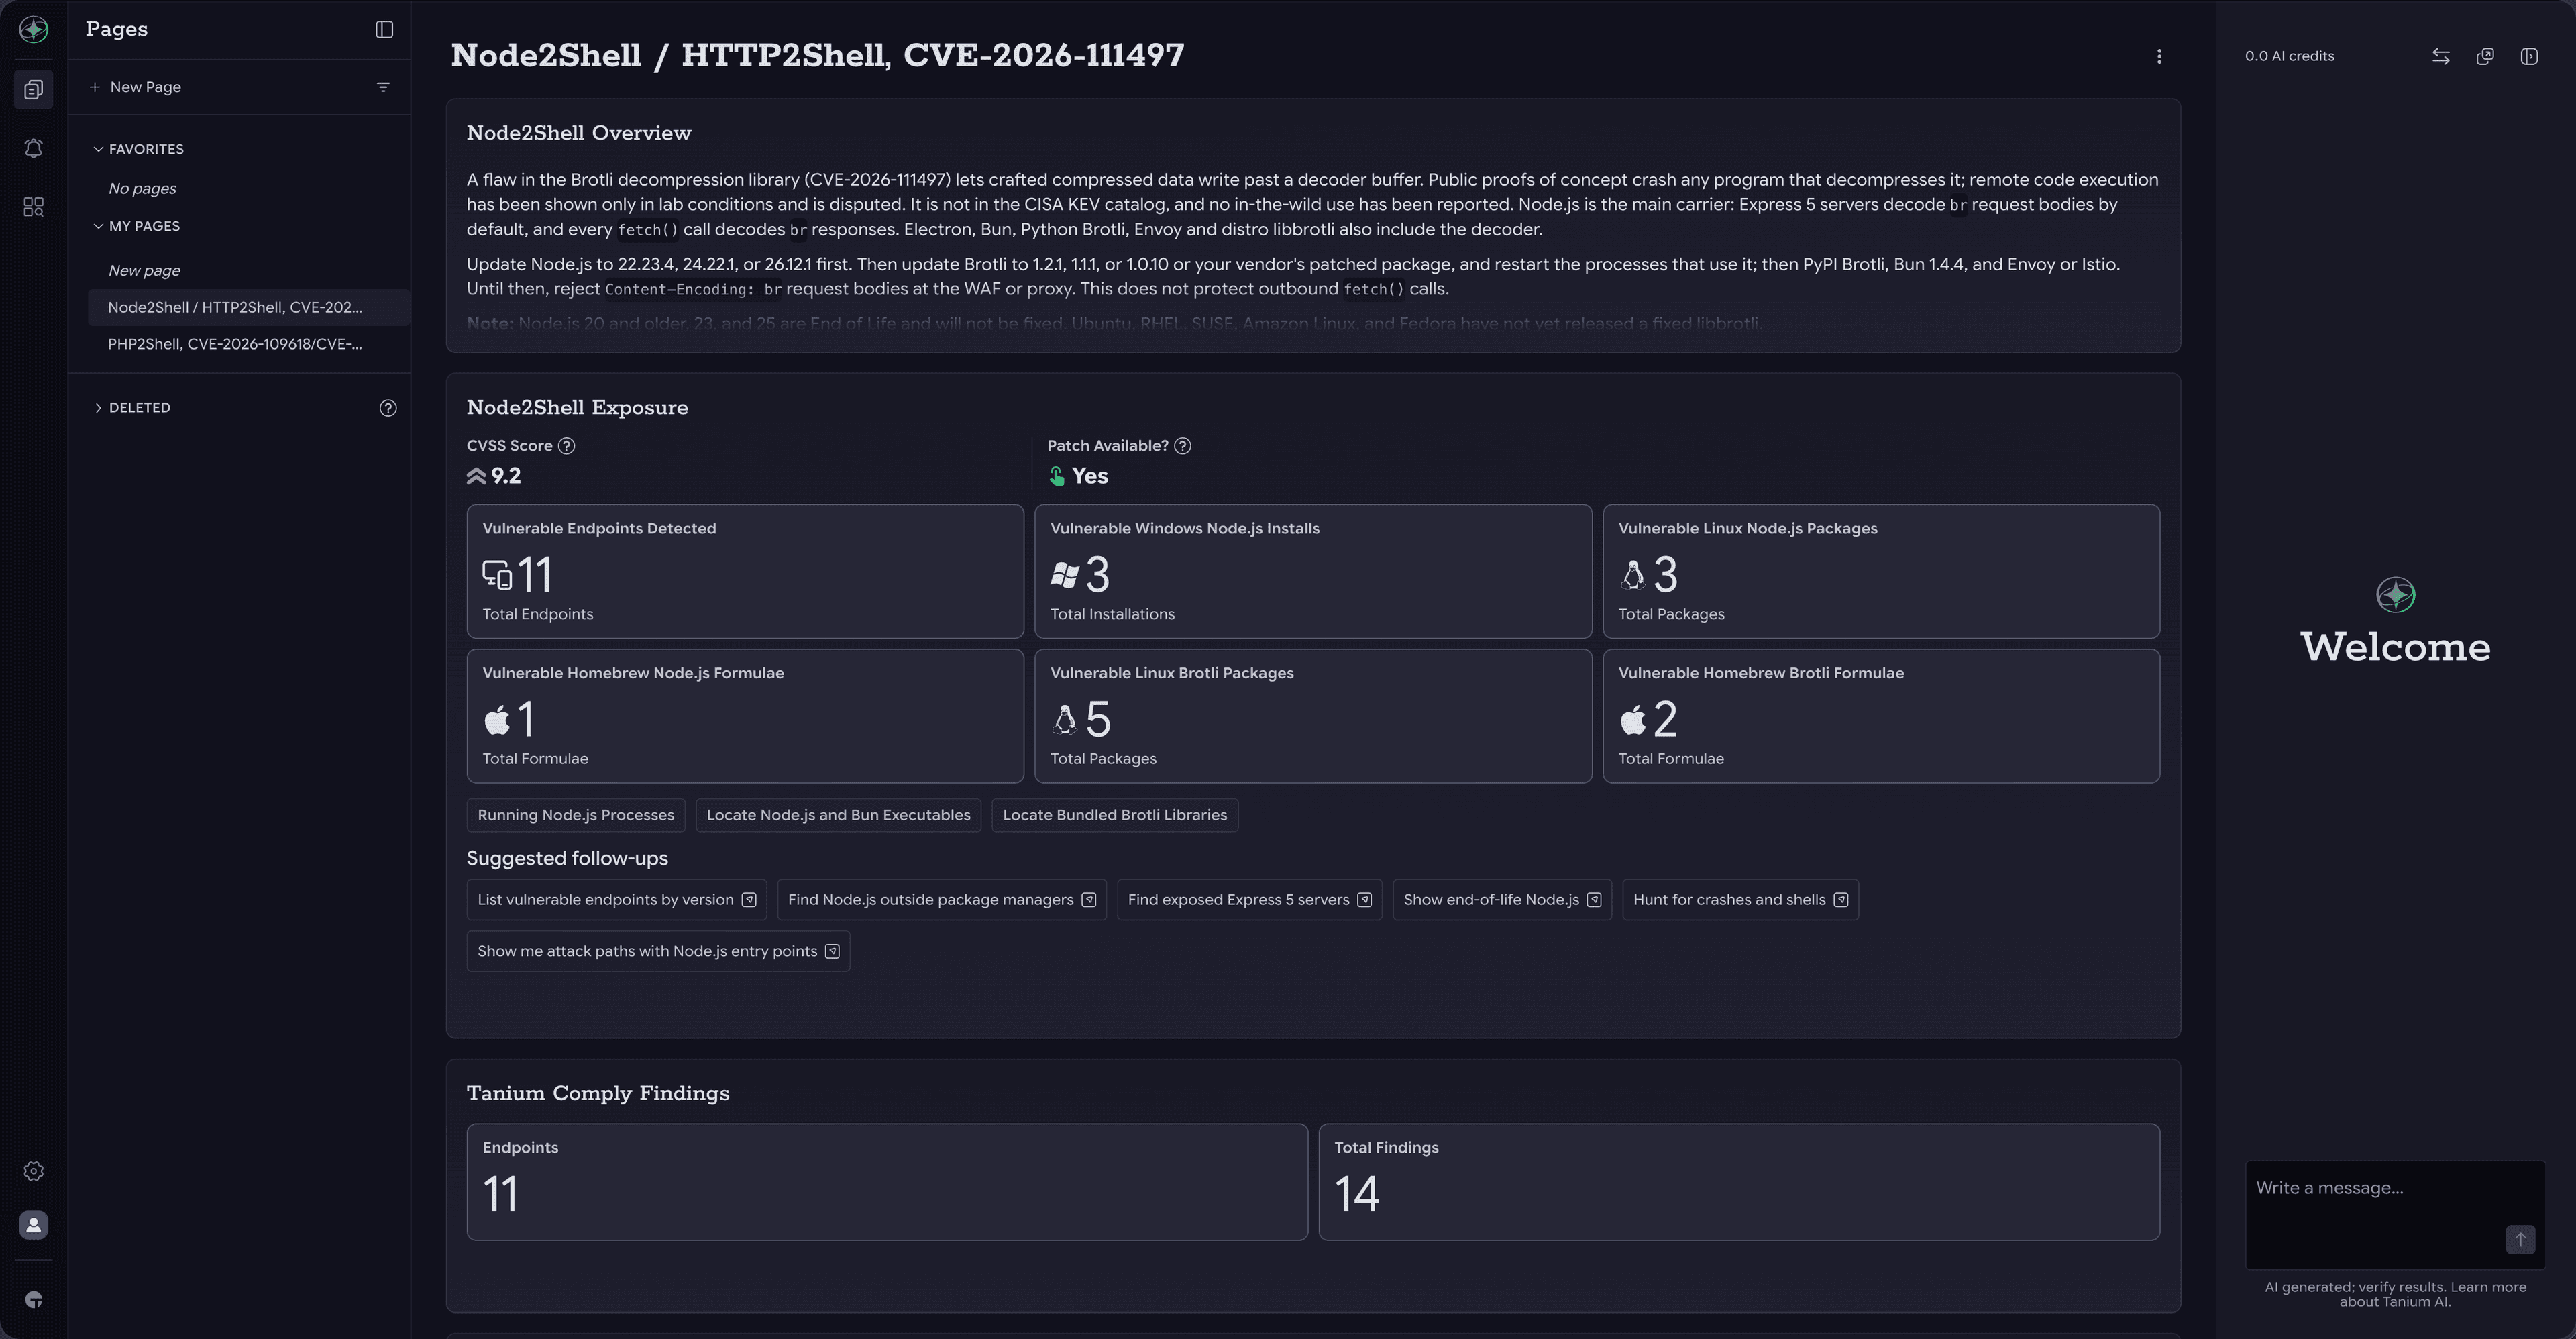
HTTP2Shell: Find and Fix Vulnerable Brotli Copies with Tanium
A critical flaw in Google's Brotli decoder (CVSS 9.2) can let a remote attacker crash or take over apps that decompress Brotli data. Update Node.js, Python Brotli and Bun now.
eMudhra CA Compromise: Find and Fix Your Exposure with Tanium
Private keys for eight eMudhra intermediate CAs can be calculated from their public certificates. Browsers block them once updated; most other software needs a trust store update.
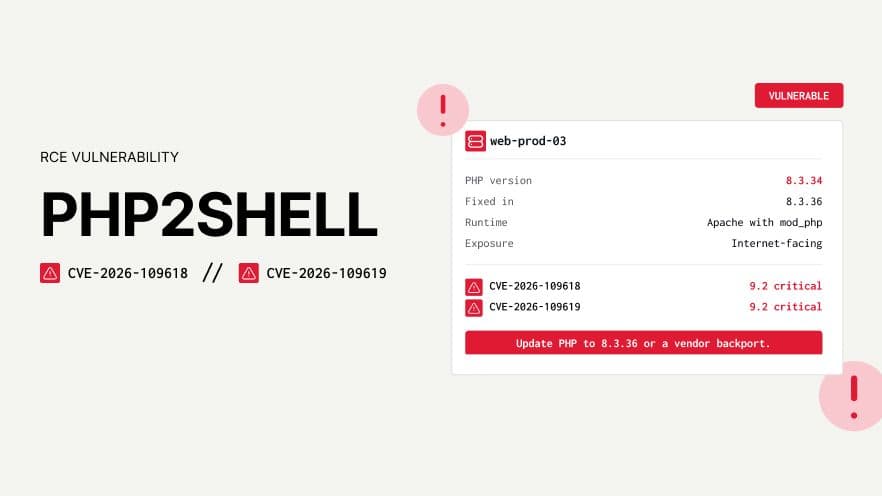
PHP2Shell: Responding to CVE-2026-109618 and CVE-2026-109619
Two critical flaws in PHP core (CVSS 9.2) let an unauthenticated attacker run code with a crafted web request. Patch to 8.5.12, 8.4.27, 8.3.36 or 8.2.35 now.
Hunt or be Hunted: Every service was unique, and that was the problem
Stacking falls apart when per-user GUIDs and profile paths make every row one of a kind.
Hunter Wins: HuntIQ Tradecraft is your new hunt library
The Hunt or be Hunted series tells the hunt stories. HuntIQ Tradecraft, now live on the Tanium Resource Center, gives you the playbooks to run them yourself.
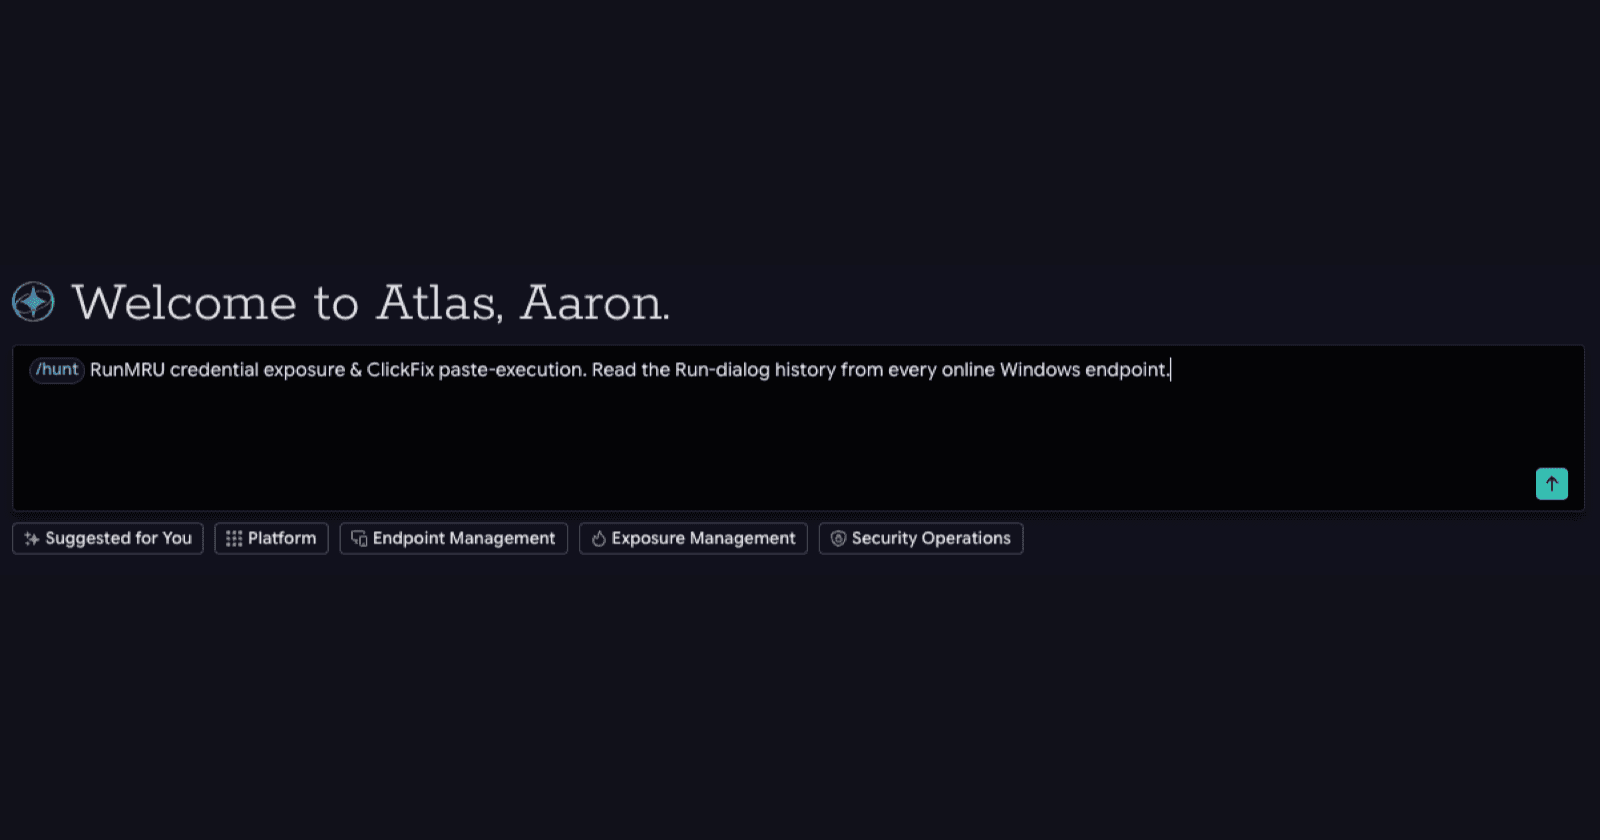
Hunt or be Hunted: Hunting RunMRU for Credential Exposure
A hunting playbook built for ClickFix went looking for pasted commands and found a working credential to a third-party portal instead.

Hunt or be Hunted: FalconFlank Zero-Day
Within 48 hours of the FalconFlank exploit's release, Tanium HuntIQ built seven behavioral detections and a single Atlas hunt prompt to catch attackers who turn CrowdStrike Falcon's own privileged clean-up against itself. See how Tanium Atlas sweeps an entire Windows fleet for the exposure in about a minute.

Hunt or be Hunted: ShieldBreak Zero-Day
Learn how Tanium HuntIQ turned a Windows Defender zero-day into a tested mitigation before a CVE was assigned.
Critical Netlogon RCE on domain controllers (CVE-2026-41089)
A critical, unauthenticated remote code execution vulnerability in Windows Netlogon (CVE-2026-41089, CVSS 9.8) lets a remote attacker run code as SYSTEM on a domain controller. Patch all domain controllers in the same maintenance window with the May 2026 security updates.
Claude Mythos security risks: What the Anthropic System Card tells us
Anthropic's Claude Mythos Preview demonstrated significant acceleration in capabilities for autonomously identifying vulnerabilities and exploit chains across major software and operating systems. Government and industry leaders are focused on understanding the real risks the model presents, and how to leverage these advanced technologies to protect and defend against adversarial use.